Gap analysis
A clear baseline against the standard or target operating model.
 910Vocational Education & Skills Development
 1039Professional Training, Qualifications & Personnel Certification
 598Consulting & Advisory
 456Auditing & Inspection
 20Testing & Analytical
 106Calibration & Instrumentation
 11Research & Development
 11Plant Design, Installation & Maintenance
 14Information Technology (IT)
 15Digitalization
 150Event Management
 14Branding & Marketing
 80Talent Sourcing & Human Capital
 80Industrial Supply
 30Mentoring, Career Coaching & Counselling
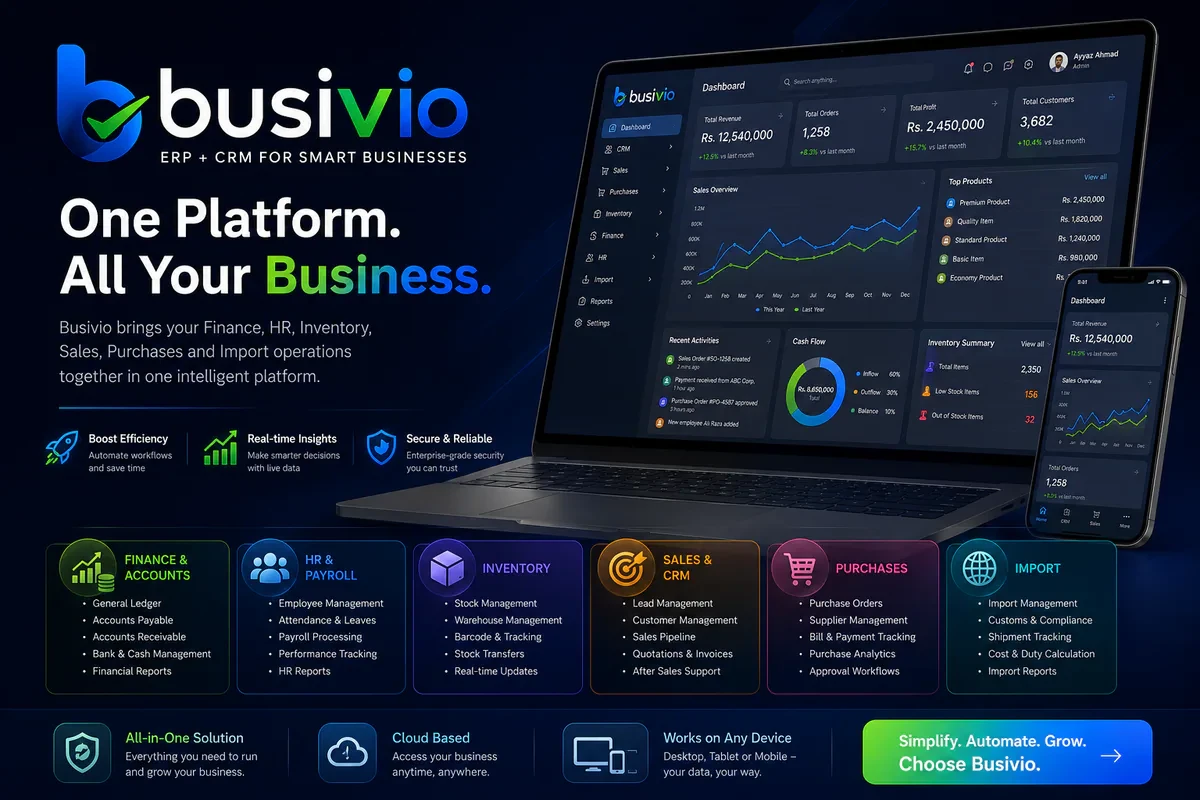 Busivio Cloud ERPComprehensive Cloud ERP, Inventory, Order Fulfillment & Financial Invoicing
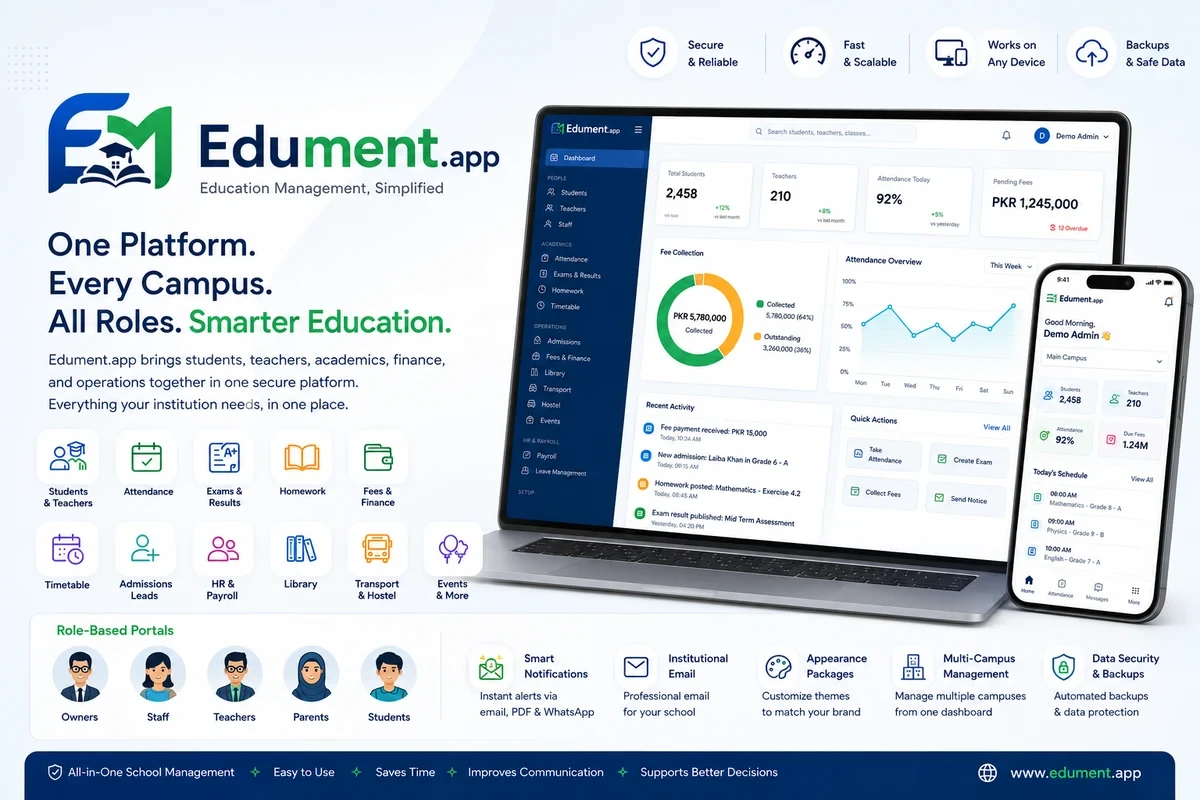 Edument Cloud School OSCloud Operating System for Modern K-12 Schools, Academies & Colleges
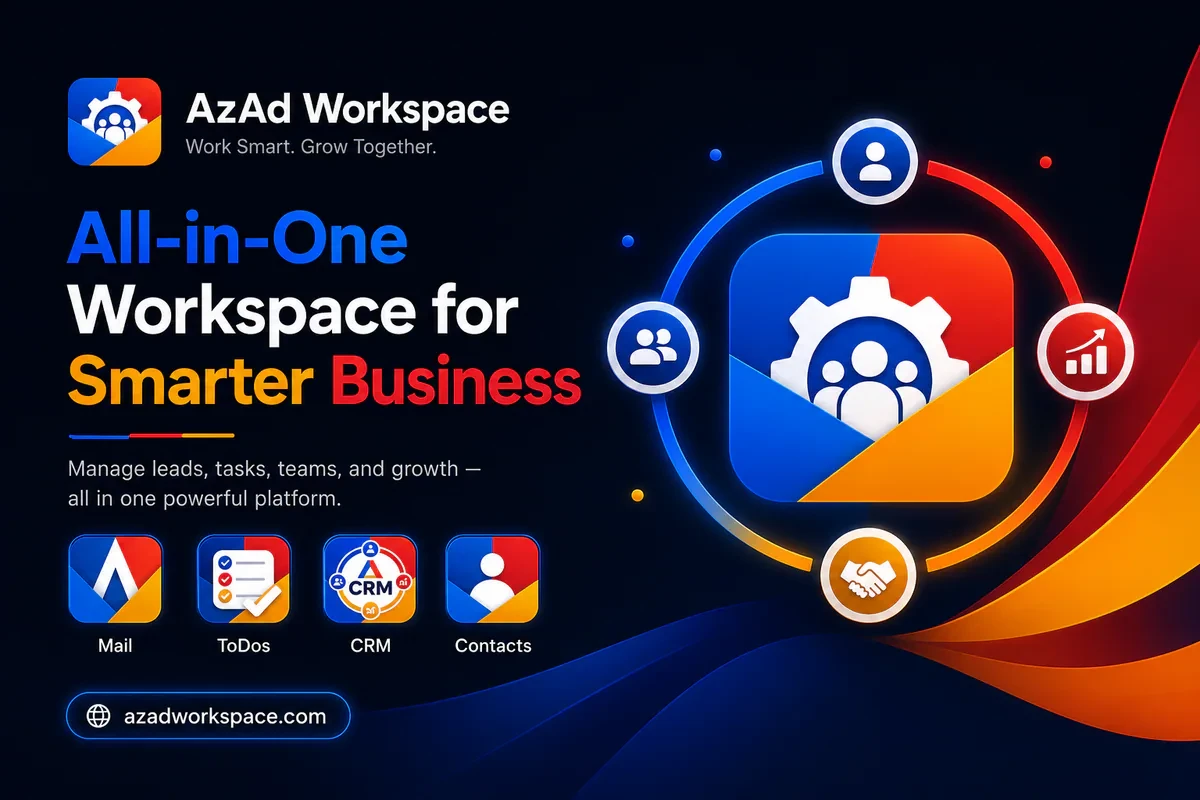 AzAd WorkspaceIndependent Enterprise Email, Collaboration, Contacts & Integrated CRM on Your Custom Domain
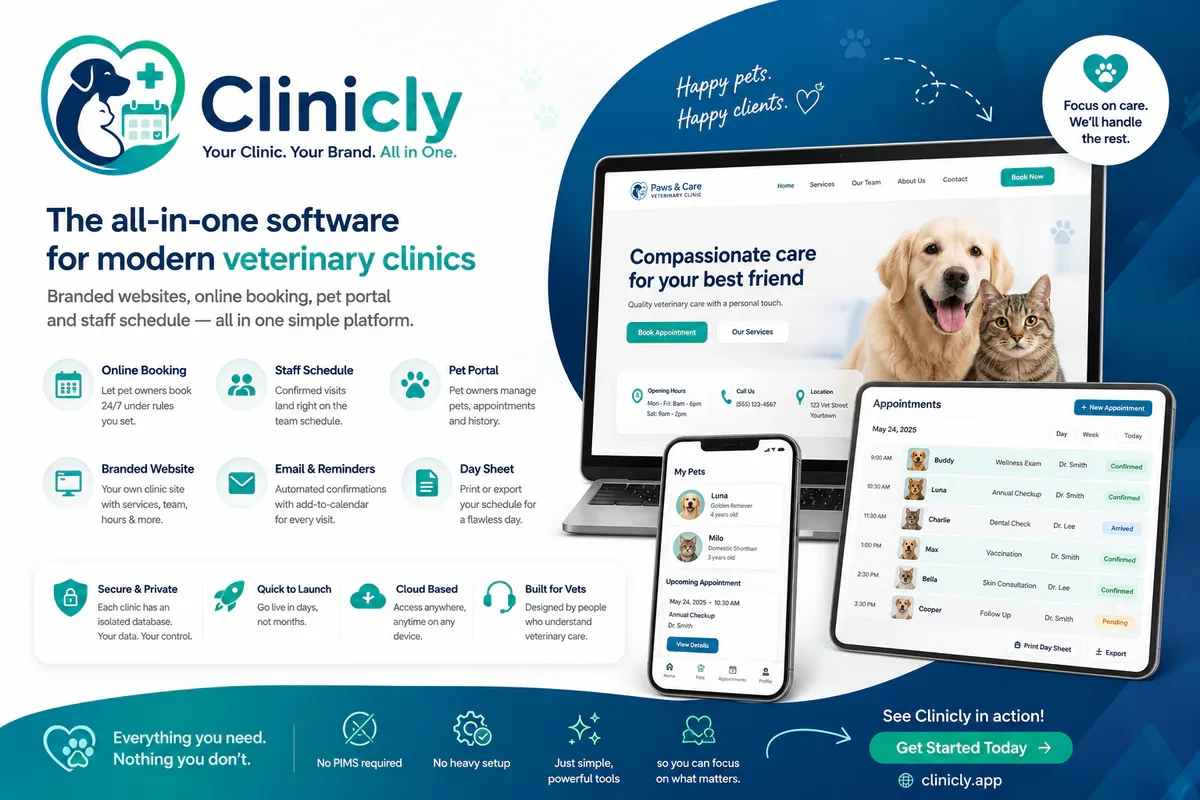 Clinicly Practice PlatformSpecialized Clinic CRM, Online Appointments, Patient/Pet Records & Staff Rostering
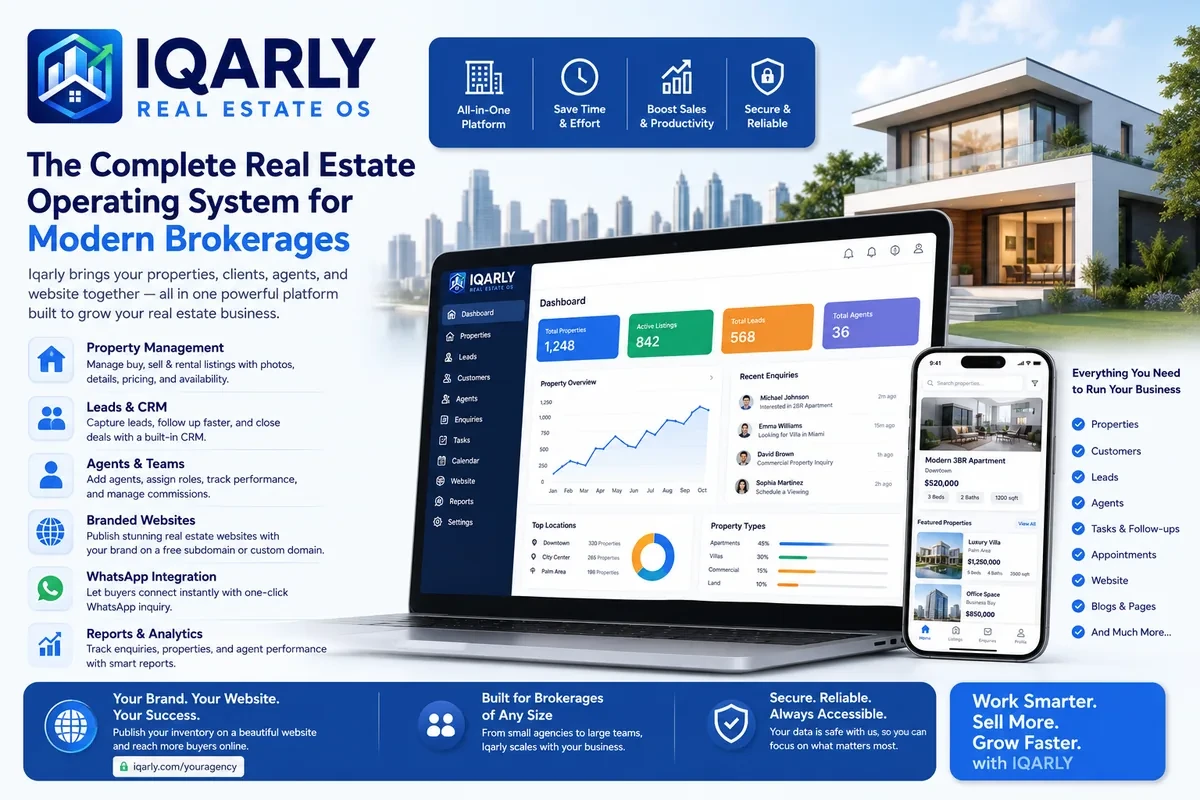 Iqarly Real Estate CRMProperty Inventory, Real Estate Deal Pipelines & Broker Lead Management
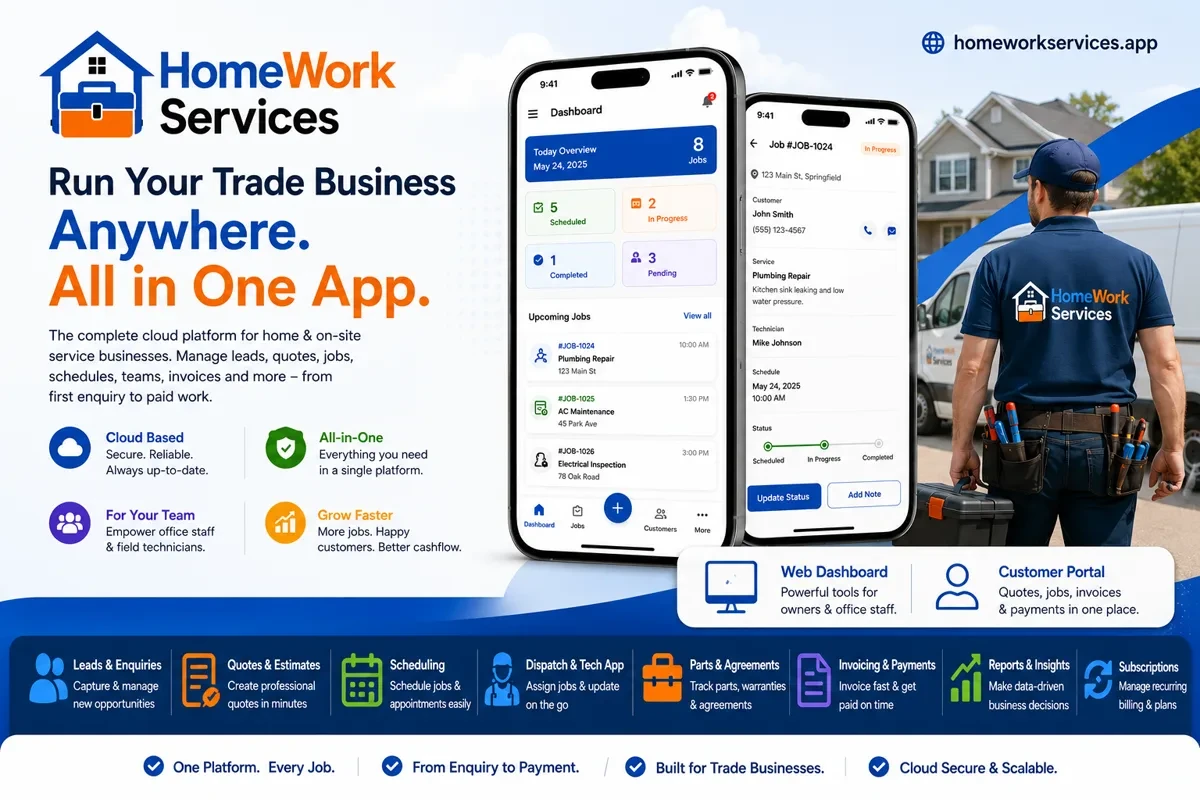 HomeworkServices Field CRMJob Dispatching, Mobile Quoting, Technician Scheduling & Invoicing for Trade Contractors
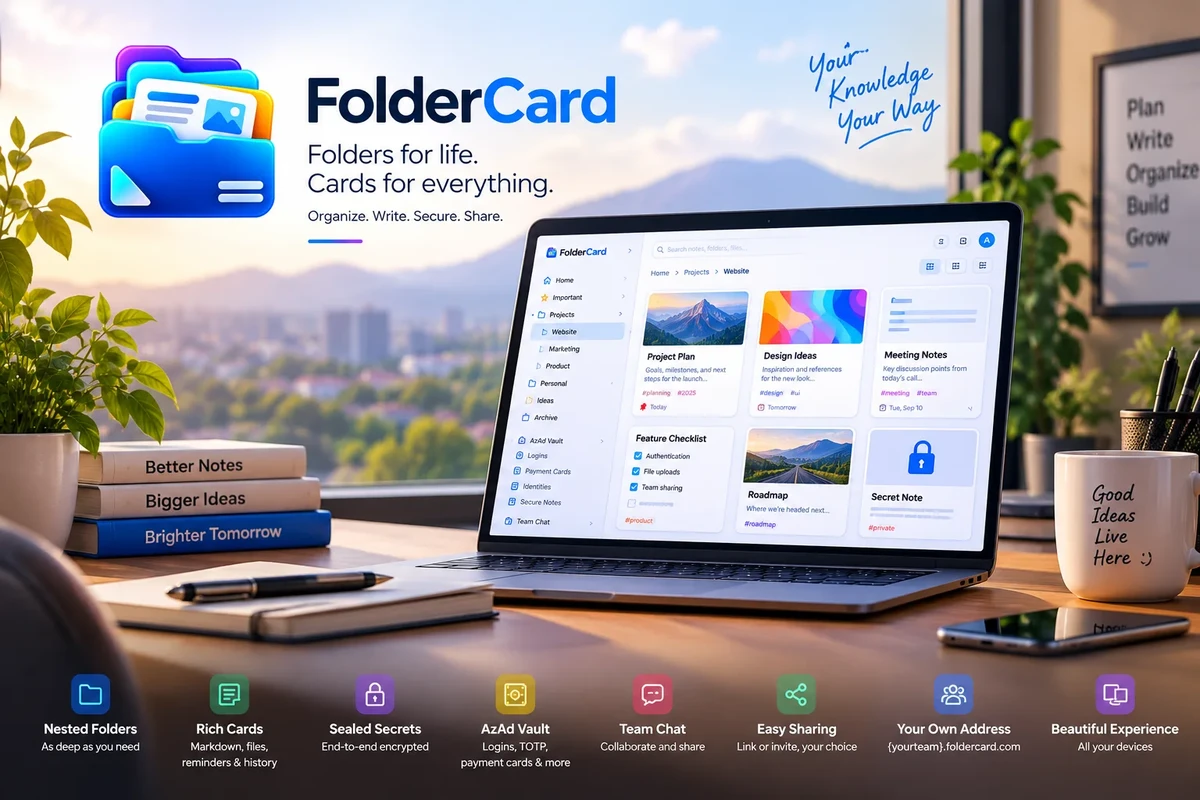 FolderCard Knowledge StudioFolders as a Menu, Notes as Cards — Structured Knowledge, Private Vaults & Team Collaboration
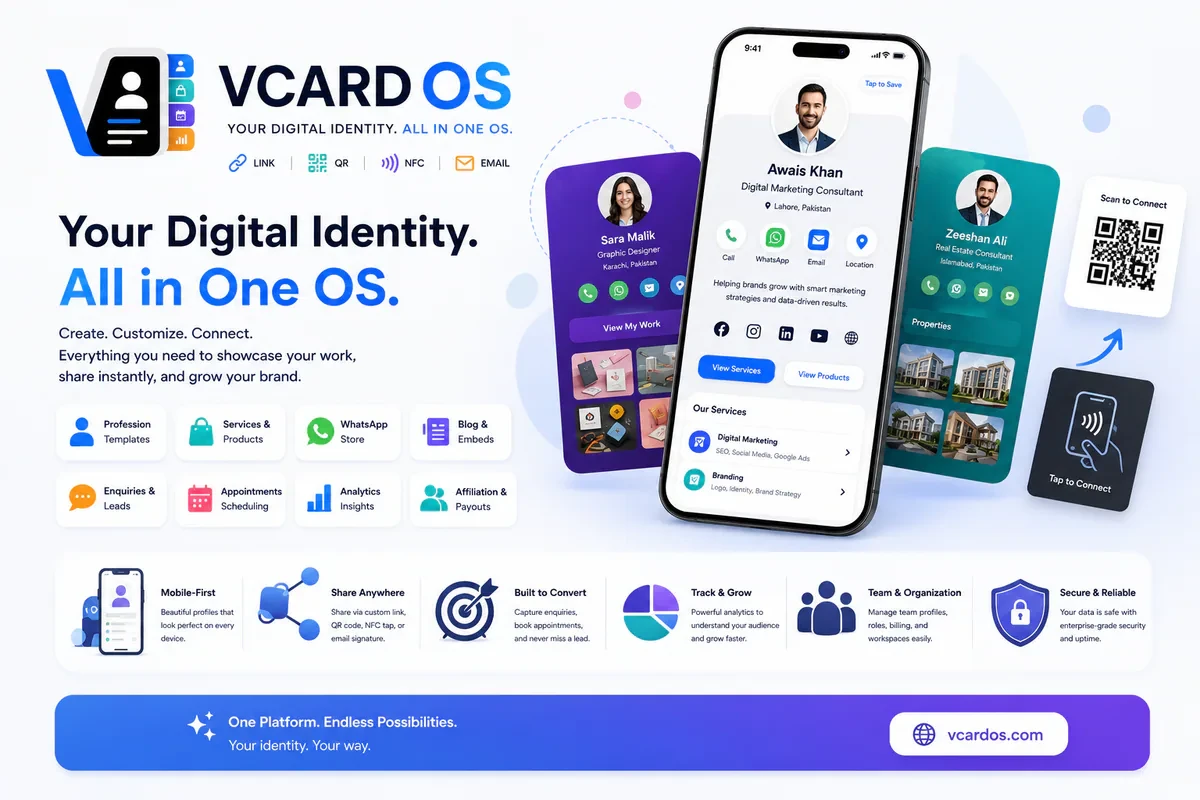 VCardOS Digital CardsNFC Smart Business Cards, Dynamic QR Profiles & Instant Contact Exchange for Modern Executives
Consulting & Advisory Services
ISO management-system, business management and financial advisory consulting that prepares organisations for certification and growth.
BUILT AROUND YOUR REQUIREMENT
Each engagement starts with the required outcome, operating context and evidence of success. The result is a focused ISO/IEC 27014 — Information Security Governance Guidance scope with clear responsibilities and handover points.
A clear baseline against the standard or target operating model.
Policies, processes, records and controls that fit how you work.
Awareness, internal auditor and leadership sessions for your teams.
Internal audits, management review and support during certification.
4 SPECIALIST CAPABILITIES
Select the capabilities that match your ISO/IEC 27014 — Information Security Governance Guidance requirement, operating context and agreed delivery stage.
A clear baseline against the standard or target operating model.
Policies, processes, records and controls that fit how you work.
Awareness, internal auditor and leadership sessions for your teams.
Internal audits, management review and support during certification.
HOW WE WORK
A defined workflow keeps the work aligned with the approved scope and makes progress, decisions and handover easier to manage.
Scope your requirementConfirm the purpose, operating context, stakeholders and expected outcome for ISO/IEC 27014 — Information Security Governance Guidance.
Define activities, responsibilities, inputs, dependencies, checks and approval points.
Complete the specialist work while keeping progress, risks and decisions visible.
Confirm the completed scope, record outcomes and agree practical next actions.
WHAT YOU RECEIVE
Documented objectives, responsibilities, constraints, assumptions and acceptance points.
Relevant analysis, coordination and technical work for ISO/IEC 27014 — Information Security Governance Guidance.
Findings, decisions, completed checks and limitations recorded for the agreed scope.
Prioritised actions for implementation, follow-up, improvement or ongoing support.
CONTINUE EXPLORING
GET IN TOUCH
Choose the type of request and share the details. The right BEMCON team will respond.